ISACA Kenya brings together a powerful community of professionals and organisations advancing governance, risk management, cybersecurity, audit, privacy and emerging technology. The 2026 conference extends that role through a five-day experience designed for both strategic leaders and practitioners.
Under the theme “Digital Trust: Securing Tomorrow’s Intelligence Today”, the event focuses on what modern enterprises must do next: govern intelligent systems responsibly, strengthen resilience, reduce digital risk, improve performance and build confidence among customers, regulators and investors.
Delegates gain insight through keynote addresses, masterclasses, case studies and peer exchange. Sponsors and exhibitors gain direct access to decision-makers, premium branding opportunities and a platform to showcase products, services and thought leadership to an audience actively investing in trust, security and transformation.
Governance models, board visibility, accountability, and digital assurance frameworks that strengthen enterprise confidence.
Practical controls for adopting intelligent technologies responsibly, safely, and in line with fast-moving regulation.
Threat readiness, cyber defense, business continuity, incident response, and resilient digital operating environments.
Data protection, third-party oversight, auditability, regulatory preparedness, and risk-informed decision-making.
Modern internal audit, controls automation, technology assurance, and evidence-led governance for digital enterprises.
Executive decision frameworks that connect secure digital transformation to growth, efficiency, and measurable outcomes.
Masterclasses, certifications, mentorship, and capability building for the next generation of digital trust professionals.
Access to emerging technologies, solution providers, sponsors, and start-ups advancing secure and trusted transformation.
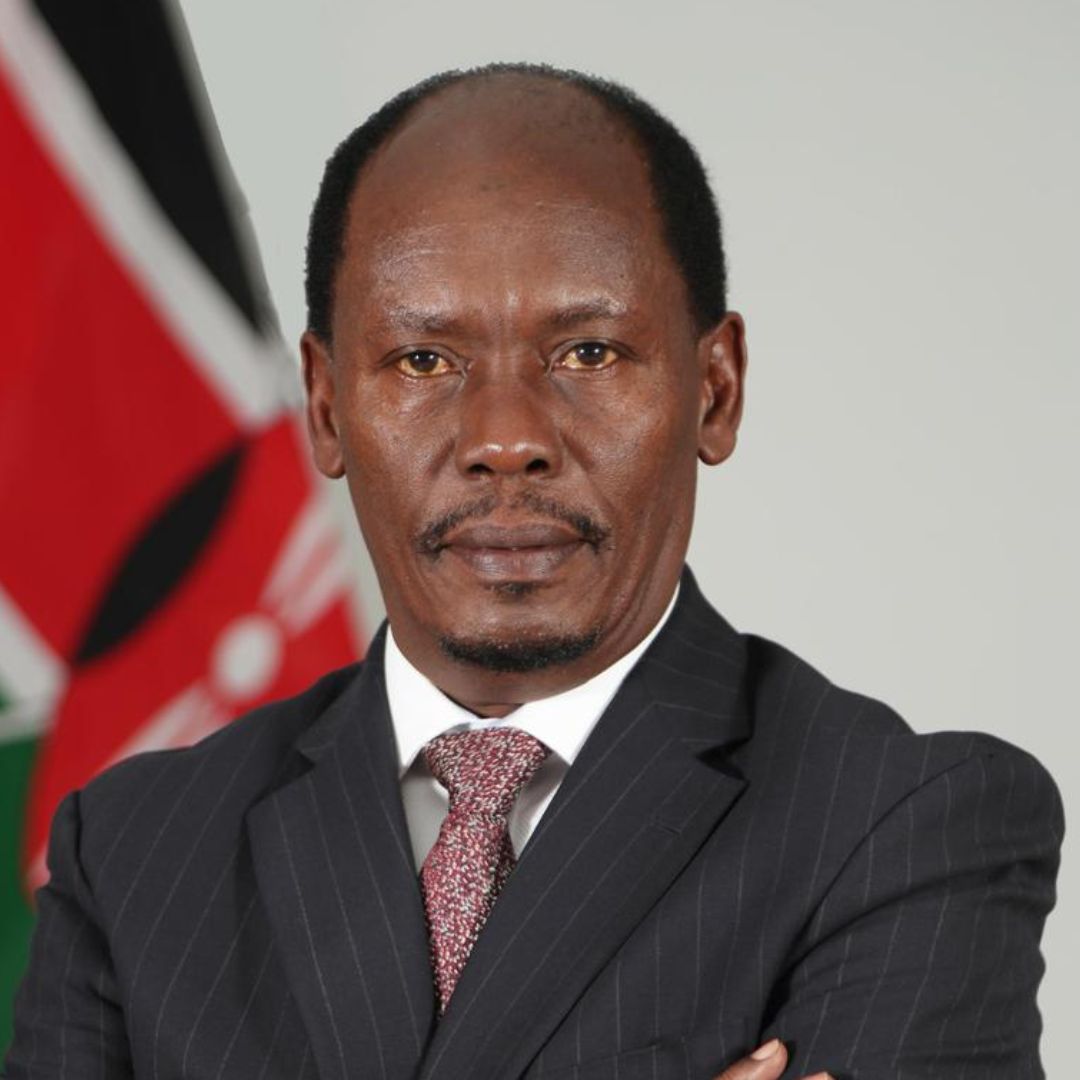
Hon. William Kabogo Gitau brings public-sector leadership and financial oversight experience to the conference’s digital trust conversation. His background across governance, public service and enterprise accountability strengthens the event’s relevance to both policymakers and business leaders navigating the digital economy. His keynote presence elevates the conference as a national and regional platform for responsible digital growth, intelligent transformation and trust-led innovation.
Hon. William Kabogo Gitau brings public-sector leadership and financial oversight experience to the conference’s digital trust conversation. His background across governance, public service and enterprise accountability strengthens the event’s relevance to both policymakers and business leaders navigating the digital economy.
His keynote presence elevates the conference as a national and regional platform for responsible digital growth, intelligent transformation and trust-led innovation.
Mr. Geoffrey Odundo is the Group Managing Director and Chief Executive Officer of Nation Media Group. He brings more than three decades of experience in financial services, strategic leadership and capital markets development. He previously served as Group Executive Advisor at CPF Group and spent nine years as Chief Executive Officer of the Nairobi Securities Exchange, where he led major market innovation initiatives including derivatives, green bonds, REITs and ESG disclosure guidance.
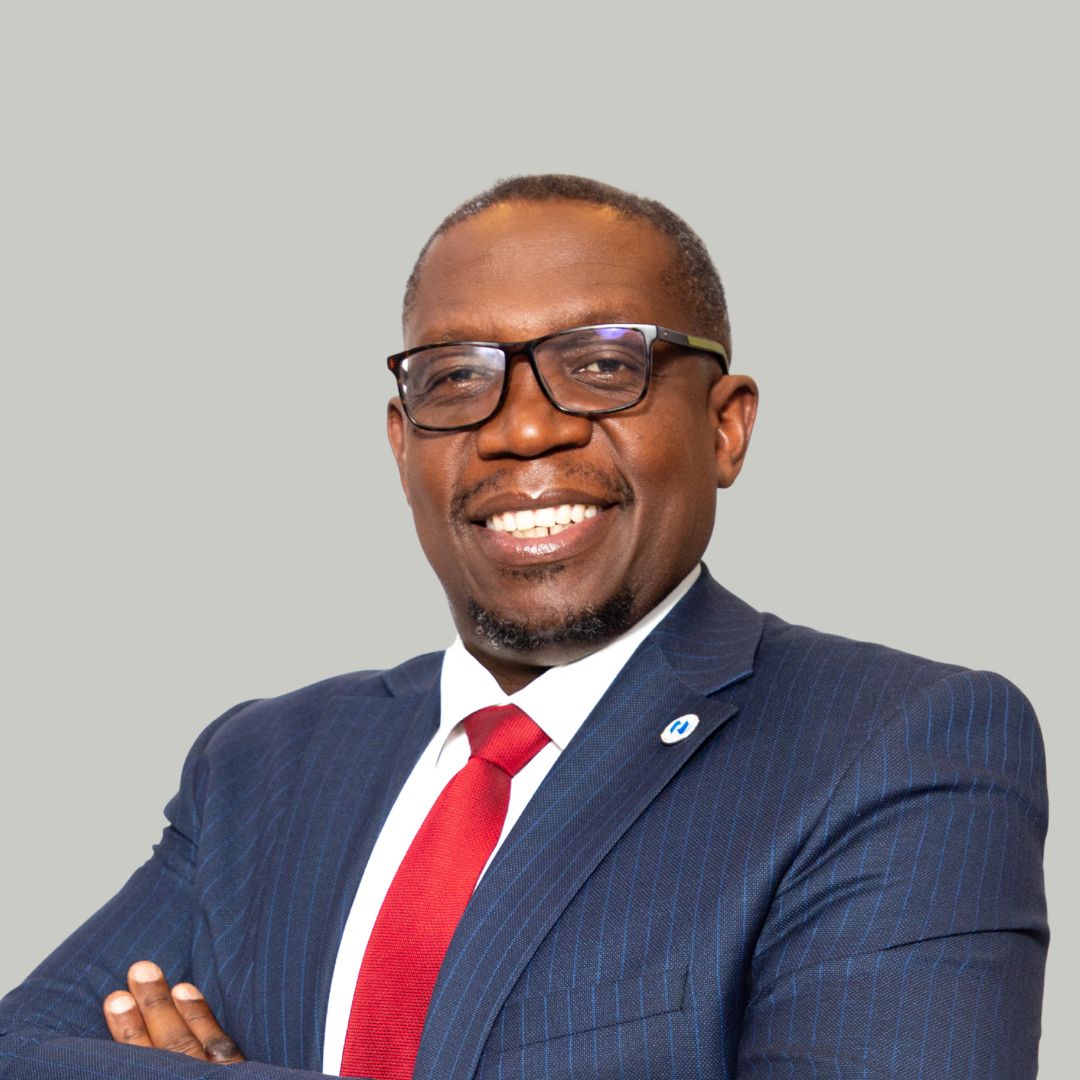
Bonface Asiligwa is the President of ISACA Kenya Chapter and a governance, risk and cybersecurity leader. He is a creative innovator and technology enthusiast with strong technical and business capabilities, focused on IT governance, cybersecurity and emerging technology. His work centres on helping enterprises use technology securely, efficiently and cost-effectively to achieve business goals.
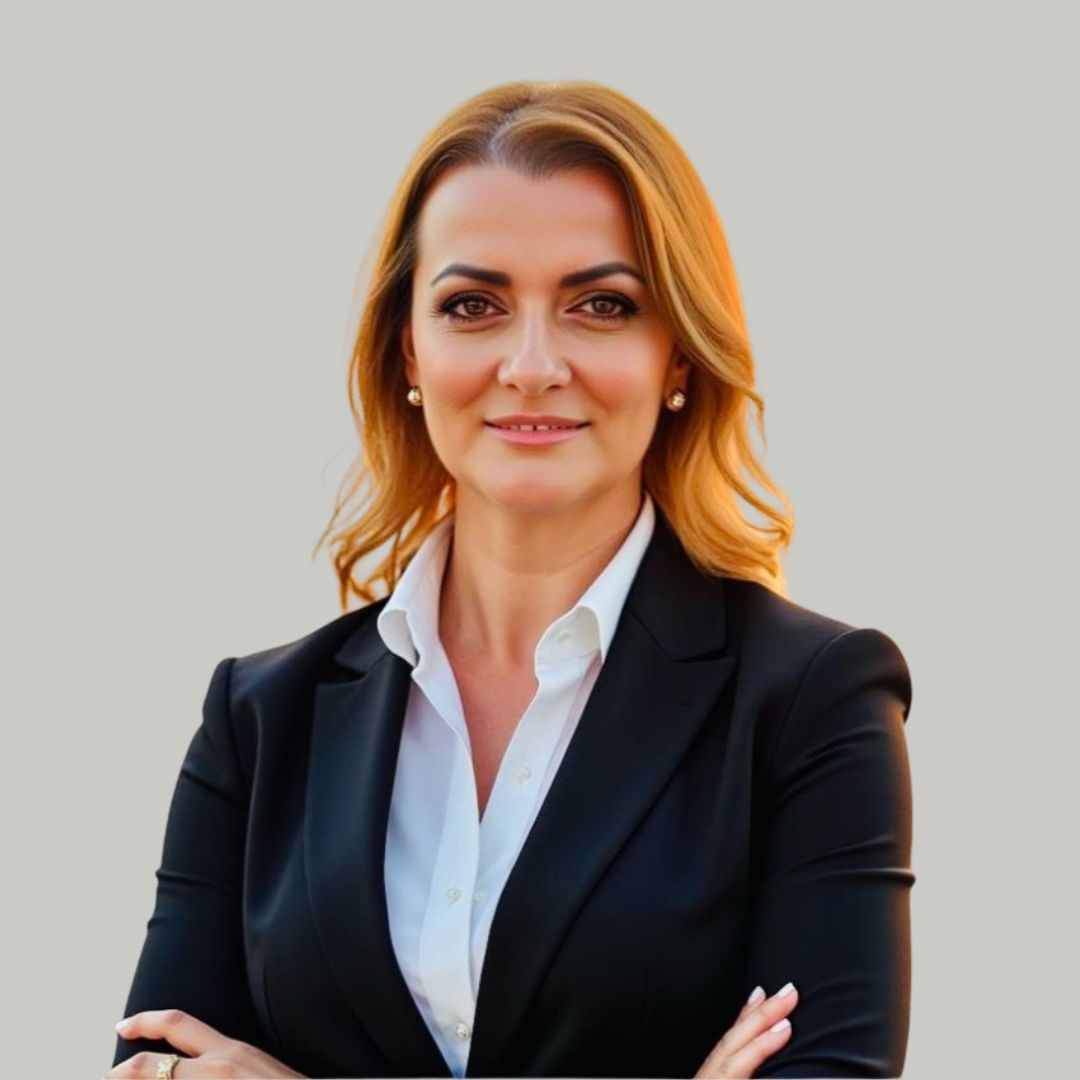
Ramona Ratiu is an accomplished cybersecurity professional with over 15 years of experience in governance, risk, compliance, and cyber resilience. She currently leads the Cyber Resilience Testing Program at Zurich Insurance, where she drives transformative projects to bolster organizational resilience against evolving threats.
Ramona serves as the Executive Advisor on Global Partnerships and Innovation Strategies for ISACA Chicago, the US ambassador at the Global Council for Responsible AI, as well as an adjunct professor at DePaul University, equipping the future generations of professionals with knowledge on IT risks landscape. Among her numerous accolades, the latest is the 2025 ISACA Technology for Humanity Award for visionary leadership in advancing cybersecurity careers, empowering women and amplifying underrepresented voices in tech.
Ramona believes in the power of collaboration and innovation to tackle complex cybersecurity and AI challenges globally. Through knowledge sharing, mentorship, and advocacy, she fosters a resilient and inclusive cybersecurity community.
Mark is an internationally known Governance, Risk, and Compliance expert specializing in information assurance, IT risk, IT strategy, service management, cybersecurity, and digital trust. Mark has a wide array of industry experience including government, health care, finance/banking, manufacturing, and technology services. He has held roles spanning from CIO to IT consulting and is considered a thought leader in frameworks such as COBIT, DTEF, NIST, ITIL and multiple ISO standards. Mark is also a two-time recipient of the ISACA John Kuyers award for best conference contributor/speaker as well as an ISACA Hall of Fame recipient in 2024. He is also an APMG product knowledge assessor for the CGEIT, CRISC and CDPSE certifications.
Tony is an accomplished Technology, AI and Cybersecurity Executive with over a decade of experience driving enterprise-wide security strategies, fostering trust, and delivering complex Digital & cyber transformation initiatives with measurable impact. Recognized for building and sustaining high-level relationships with regulators, governments, C-level executives, and industry leaders, blending strategic vision with hands-on execution to support business growth and policy influence. A trusted advisor with a proven track record in shaping national policies and digital roadmaps, including contributions to Kenya’s Digital Master Plan, Kenya Data Protection Act and National Cybersecurity Strategy while championing public-private partnerships and cross-sector collaboration. I am a commercially-focused tech leader with deep Kenya market experience. I drive revenue growth through product-led GTM, strategic partner ecosystems, and talent development. I am agile and highly entrepreneurial with a bias for action, with a talent for inspiring and leading teams to achieve exceptional outcomes. Renowned for representing organizations at the highest levels through keynote speaking, media engagements, and panel participation, effectively shaping public perception and reinforcing leadership in digital and cybersecurity. Adept at blending technical expertise with diplomatic acumen, I bring a unique ability to engage with governments, regulators, and senior executives, fostering trust and credibility in digital initiatives.
Dr. Mugambi Laibuta is a legal professional, academic, and thought leader in privacy, data governance, and emerging technologies. He brings over 17 years of experience in law practice, legislative drafting, and policy development, with a proven record of advancing rights-based governance frameworks in Kenya, Africa, and beyond. His current work focuses on data protection, constitutional law, and digital transformation. He advises institutions on compliance, governance, and regulatory strategies while leading multi-stakeholder engagements, strategic litigation, and capacity-building initiatives that strengthen trust in data use and emerging technologies. Dr. Laibuta has previously contributed to high-level constitutional reform processes in Kenya, South Sudan, Somalia, Sudan, and Chile, and has supported governments, development partners, and civil society with legislative, policy, and regulatory reforms. He has also served in senior advisory roles, including Director of Legal Services and Acting Director of Health at the Council of Governors, and has lectured widely on legal drafting, data governance, and technology law. He holds a PhD in Law from the University of the Witwatersrand, an LLM from the London School of Economics as a Chevening Scholar, and is a Certified Information Privacy Manager (CIPM). He also serves as Chairperson of the Data Privacy and Governance Society of Kenya.
Mr. Jessy K. Maruti is the Chief Executive Officer of the ICT Authority, appointed on 16th February 2026. He is an accomplished digital transformation leader with over 18 years of experience shaping ICT policy, strengthening national digital infrastructure, and driving innovation across the public sector.
Prior to his appointment, he served as Head of Public Sector at Telkom Kenya, where he spearheaded strategic connectivity and ICT infrastructure programmes supporting ministries, departments, and agencies nationwide.
He holds a Master of Science in ICT Policy and Regulation and a Bachelor of Science in Telecommunications and Information Technology, and is currently pursuing a PhD in Business Innovation and Technology Management. His professional expertise spans governance, project management, and information systems audit, strengthening his ability to translate national ICT strategy into measurable impact.
Under his leadership, the ICT Authority continues to champion technology as a catalyst for economic growth, institutional excellence, and inclusive national development.
He is committed to building a digitally empowered public sector that delivers efficient, transparent, and citizen-centred services.
Christine Keriga is a Risk Management professional with extensive experience in Integrated Risk Management in Financial Services and Telecommunication industry. She is currently the Principal Officer, Insurance and Risk Management at Safaricom Plc. Her work spans in Integrated Risk Management, supplier risk oversight, and emerging risk assessment across highly regulated and rapidly evolving environments.
Christine has been instrumental in strengthening third-party risk management frameworks, including supplier due diligence, physical validations, and ongoing risk monitoring, with a strong focus on governance, compliance, and operational resilience. She brings practical experience in aligning risk frameworks to global standards such as ISO 31000 and COSO, while embedding them into business strategy and decision-making.
With a growing focus on emerging risks, Christine is actively involved in assessing how the adoption of AI through third-party ecosystems is reshaping organizational risk profiles.
Victor Ndede is a lawyer and privacy professional currently serving as the Head of Programmes at Amnesty International Kenya.
As Head of Programmes, Victor provides strategic direction and support to multidisciplinary teams, deepening the Amnesty Kenya’s impact across four critical programs: Technology and Human Rights, Civil Liberties, Equality and Anti-Discrimination, and Movement Building.
A Tech & Human Rights leader, he provides legal and policy analysis and thought leadership to inform Amnesty International Kenya digital rights programs and campaigns in Kenya. He leads a talented program team working on strengthening data governance in Kenya and East Africa besides working on digital rights for children and young people. He is an advocate for a safe internet for all persons.
His leadership is informed by an extensive background in legal research, legislative engagement, and human rights monitoring.
Victor is an Associate Fellow of the Royal Commonwealth Society and was recognized in Kenya’s Top 40 under 40 Men 2025. He serves on the advisory boards of several non-profits and initiatives on the African continent.
Gladys is a seasoned technology risk, information security, and governance leader with over 25 years of experience across IT service management, governance, risk, and compliance. She has led and advised on large-scale enterprise IT transformations and security programmes within complex, multi-country environments across Africa and globally.
Gladys holds a Master of Science in Strategic Business IT and is a Platinum Member of ISACA, with professional certifications including CISA®, CISM®, PRINCE2® Practitioner, and ISO 27001 Information Security. She brings strong board-level and regulatory experience, having previously served on the ISACA Kenya Chapter Board, where she supported information security skills development and regulatory advancement.
Currently, Gladys is Head of Information Technology at KPMG East Africa. She previously worked with the Global Information Security Group at KPMG International, working with geographically dispersed teams to advise Chief Information Security Officers on information security, privacy, and compliance across EMEA and Asia-Pacific. She is also a part-time teaching fellow at Strathmore Institute and serves on multiple boards, contributing to governance and fintech innovation.
Eric Mutunga Ngei is the Group Cybersecurity Head at KCB Group.
Ngei provides strategic leadership for the Group Cybersecurity organization, focusing on defining and delivering the cybersecurity vision and strategy. They oversee budget planning, resource management, and cybersecurity investment to mitigate cyber risks, positioning cybersecurity as a key enabler of digital trust and a competitive advantage for KCB. Ngei leads the group-level cybersecurity team in designing, implementing, and improving the cybersecurity strategy, cyber defense capabilities, and enterprise security architecture. They ensure cyber risks are detected and remediated effectively, overseeing the delivery of expertise in strategic program management, technical security domains, assurance, and security operations.
Previously, Ngei served as a Senior Information Security Consultant at EY, where they conducted enterprise security assessments, developed enterprise architecture, and performed attack and penetration testing. They also contributed to studies on cross-border mobile financial services and card interoperability in East Africa. Earlier in their career, Ngei was an IT Security Specialist at KCB Group, focusing on enterprise threat and vulnerability management, identity and access management, and developing information security policies. They also gained foundational experience in auditing and accounting at Mbaya & Associates
Leah Kimata is a distinguished executive leader with over 15 years of experience driving cyber security, technology risk governance, and digital transformation across Africa, the Middle East, and global markets. She has led enterprise-wide strategies in financial services and fintech, with a proven track record in cyber and IT risk governance, resilience, and enabling data, analytics, and AI adoption.
Formerly Executive Director for Cyber & Technology Risk Governance at Standard Chartered Bank, Leah oversaw large-scale digital modernization, resilience frameworks, and regulatory-aligned risk programs. She is recognized for her ability to translate complex technical concepts into actionable board-level narratives, balancing innovation with compliance and commercial growth.
Leah holds an MSc in Risk, Crisis & Disaster Management from the University of Leicester and multiple professional certifications including CISA, ISO 27001 Lead Auditor, and PRINCE2 Practitioner. She is passionate about inclusive leadership and mentorship, actively championing diversity advocacy and sustainable talent pipelines in the technology sector.
She has partnered with global startups, investors, and regulators to build forward-looking frameworks that integrate resilience, risk quantification, and human-centric compliance. At the ISACA Kenya Annual Conference, Leah will bring her strategic insights to the panel on “Integrating AI Governance, Risk, and Compliance” to help organizations navigate the evolving landscape of digital trust
Oscar is the Deputy Data Commissioner at the Office of the Data Protection Commissioner. He is an Audit and Investigations professional with over 18 years of experience working in both the private and public sectors. Oscar holds a Master of Business Administration (MBA) from the University of Nairobi and a Bachelor of Science in Computer Science. He has extensive experience having worked in the banking industry and in one of the Big Four Audit Firms as a consultant. He is a Microsoft Certified Systems Engineer (MCSE) and a Certified Information Systems Auditor (CISA).